Wednesday, May 8, 2013

Desktop Phishing - Step by step tutorial


Desktop Phishing - Step by step tutorial-SHINE SREEDHAR

Phishing - Creating,uploading and using fake login pages


If you do not know what exactly phishing means , I highly recommend you to read my post on basics of phishing here.
I could simply give you the fake page generators or already made fake web pages but I want you to manually create yourself.

First, I shoud tell you the basic methodology of making phishing page of any website. In a website where the users are supposed to enter/submit any data (data might be email,password or anything), there is a piece of code in html code called as action form. It looks like this
<form method="POST" action="something">.
You can find this out by simply viewing the source of web page. Right click on webpage to do so. "something" here in the action field is name or path of the file where submitted data goes. So the idea of fake login page is simple. Just download the webpage on your computer, modify the action field to change the path where data goes according to yourself, upload this modified webpage on any web hosting site and you are done. :)

I have taken example of gmail.

Download a php file and a text file from here which would be required. Password:explorehacking.com

Setps to make a phishing/fake login page :-
1. First of all, sign up for a account at any free webhosting site like my3gb.com,ripway.com,110mb.com etc.
I have chosen my3gb.com
2.Goto www.gmail.com.  Click on 'Save page as' option  and save the complete web page. You must have got a html file and a folder in which there must be two images.


3. Open the html file in any text editor like wordpad or notepad. Press "Ctrl+F"  to search for word "action".


4. Replace the link in action field by "explore.php" and save it.
5. Go to File Manager and Upload this html file ,hacked.txt , explore.php  on your web hosting site.

Note: Make a new directory with name exactly same as name of folder in which images are there.
 Upload the images in that directory.

Now you can test whether it works or not. Just visit your fake login page.It must behttp://username.my3gb.com/filename.html. Enter any username and password , you will
be redirected to real gmail webpage.The data must have been saved in hacked.txt

Note: You can see the code of explore.php . There is a line like header:"location: path". It is
actually the path where victim would be redirected after submitting data. You can change it as per your need.

I hope the logic and methodology of creating a fake/phishing page is clear to you. You can use this for any website. If you are really lazy or facing problems in making phishing page of any other website, Kindly mention in comments and I have an other option for you.
Warning : Your account might be removed any time because of violating terms and conditions of site. So always have a back up of your data.
Note: Read about advance way of phishing that is Desktop Phishing here.

Remote Keylogger - configure and use


Remote Keylogger - configure and use

Keyloggers are the best to spy upon anyone but many beginners find problem in using remote keyloggers . So in this post , I will be showing you the same.Remote keyloggers are very easy to use in comparison to trojans where the concepts like IP addresses, port forwarding are involved.  I highly recommend you to read the basics of keyloggers here . 

Requirements :-
1. Download a free remote keylogger 'Ardamax' with its serial keyherePassword:explorehacking.com. Antivrus might detect it as a virus but dont worry.

2. Signup at any webhosting site supporting FTP (file transfer protocol) and note down your ftp host name. 
For example , I have signed up at www.my3gb.com and ftp host name is  username.my3gb.com . 

We are actually gonna create an executable(exe) file, which would be given to victim and he is supposed to run it. The keylogger would be installed on his computer and we would be getting automatically keylogs/screenshots in our web hosting site ftp account

I have added the self-explanatory pictures, follow them.


After entering registration key, click on Remote Installation
option . If it still says that its  unregistered version, restart computer.

Keylogger would run invisibly on victim's computer. Victim have would have to
press Ctrl+Shift+Alt+H and enter the password you have set to make it visible.


FTP hostname may be different for different web hosting sites. Mostly it is username.webhostingsite.com . You can specify any remote folder in which you wish to get logs. After filling all details, click on 'Test' and you would get any test file to make sure that  information you filled is valid and FTP connection is okay.

So you have got an exe file which is detectable as a virus by antiviruses. Now use social engineering to make victim to click on this exe file and hopefully you would start getting the keylogs and screenshots in your account. You cant send it as an attachment in email ID. The good way is to uplaod it on any uploading site and give him the dowloading link.

Email Bombing


Basics of working of Email ( You can skip this part)

Email stands for Electronic Mail. Email sending and receiving is controlled by the Email servers.Email service providers configure Email Server before anyone can Sign into his or her account and start communicating digitally.Users from across the world register in to these Email servers and setup an Email account.


Email Travelling Path :-
Let’s say we have two Email providers, one is gmail.com and other is yahoo.com, ABC is a registered user in gmail.com and XYZ is a registered user in yahoo.com.
• ABC signs in to his Email account in gmail.com, he then writes a mail to the xyz@yahoo.com and sends the message.
• But what happens behind the curtains, the Email from the computer of abc@gmail.com is forwarded to the Email server of gmail.com. Server of gmail.com then looks for yahoo.com on the internet and forwards the Email of the yahoo.com for the account of XYZ@yahoo.com. Yahoo server puts that email in that account.
• XYZ then sits on computer and signs in to her Email account.Now she has the message in her Email inbox.


 Sending Fake/spoofed Email -:  Fake or spoofed email means the email from any email ID. It doesn't matter whether the sender's email really exists or not. Sender's email ID can be anything@anything.com. 

   Read the disclaimer before proceeding

Methods :-

1. Using Open Relay servers :  An open relay server is that which allows people to send email by connecting to it. User connect to it via telnet and instructs server to send email. This method is outdated or simply I should say that, it doesn't work. I would not talk about it more.

2. Using Websites : There are numberless websites that provide free service to send fake emails. But the problem is that they attach the advertisments along with your email.  But the best two, I have found that do not attach the advertisments.

www.emkei.cz      {have some advance options}
www.hidemyass.biz/fake-mailer/

3. Using mail sending scripts : The PHP contains mail sending function which allows us to send email with fake headers.
Download a php script from here.
We just need to upload the mail sending script on a web hosting site. It doesn't work on every webshosting site because there is no email sending support.  I have tested x10hosting.com (could take upto a day for account activation) , it works perfect. Some of the other are www.000webhost.com,byethehost5.com

Note: This script contains options of sending spoofed email, spamming and email bombing. Your hosting account might be immediately suspended on spamming/bombing. But it works perfect if you have any your own premium web hosting account. If you want to try email bomber, I could let you to use my own if sufficient people request in comments.

What is Email Spamming and Email Bombing ?

Email Bombing as clear from the name is sending the mass emails that is large number of emails to a email ID in a single click. Email spamming is like sending an email to large number of email IDs in a single click. These activties are performed mainly for the advertisements of the products or services provided by a company. Many spammers spam to collect individual's personal information through some stupid things like 'fill these details to get your lottery amount' and that information is sold to businessmen looking for the people of different categories. There could be many more reasons of spamming. Spammers use automated tools to collect as many emails available on websites,forms,chat rooms and send spams to them.

How to identify whether an email is real or spoofed ?

It can be done by checking headers. Email headers is simply the text which contains the information about the mail servers that the email encountered in its path from the sender to receiver. It contains a lot of other information too.
Note: I am just telling you a few points about this so that you would just get an idea about the approach. This may or may not depend on some factors.

We can view email headers in gmail by clicking at 'show orignal', in yahoo by clicking at 'Full headers' and such kinds of options in other email service providers.

If  you get an email displaying sender's email like someone@gmail.com, someone@hotmail.com, someone@yahoo.com . Then it should be orignated from gmail,hotmail and yahoo servers respectively. But if it doesn't, the most probably the email would be fake. 

I will show you by an example, I received three emails in my gmail inbox from sender's address "someone@gmail.com."  Sender's address shows me that they should have been orignated from gmail/google server, if they would be real.

Note : There is a field called "Return-path" in headers.  If the email ID shown in this field and email ID you get as sender's email ID doesnt match, then the email is surely fake.


Can we get sender's IP address from Email Headers ?

We may or may not. Gmail, yahoo normally do not reveal sender's IP address. But when we send an email from a php script,  the headers might reveal Sender's IP. The conclusion is that answer to this question varies from different email service providers and the way how email is sent.

Can we trace sender's location, if we get his IP address ?

The IP address could only tell that which Internet Service Provider (ISP) is used by sender. Further details can not be revealed without the help of that ISP. Normally the Public IP is dynamic that is it keeps changing. We need to ask ISP about the user who was assigned that IP at the time email was sent. If sender has purchased a static IP address, it doesn't matter that when exactly was email sent. He could easily be traced.

How to secure your system from Keyloggers_ by SHINE SREEDHAR


What is Keylogger?


Keylogger is one of spyware which will what type you through the keyboard and send it to hacker who send the keylogger. Hackers mainly use keyloggers to steal your passwords, credit card numbers and other confidential data.  So whenever you type the username and password in gmail,online banking sites, it will send the username and password to hacker.  


How to Protect?


In order to provide security for your system,you must have


Good AntiVirus:
This is basic and best step to protect your system from keylogger.  So buy a licensed and best antivirus which is currently in market.  My suggestion is Kaspersky, Norton or Mcafee.  Don't forget to update regularly.
Note: Don't use trial or cracked pack ,it is worthless to use.

Good Spyware:
Since keyloggers are basically spywares, if you are a frequent user of Internet then you could be exposed to thousands of keyloggers and spywares. So you should use a good antispyware such as NoAdware.


Antilogger can be Handy

Antiloggers are programs that detect the presence of keyloggers on a given computer. Zemana Antilogger is the best antilogger.

Online Scanning

When ever you receive a suspicious file, you scan it with online scanners such as Multi engine antivirus scanner which scans your file with 24 antivirus engines and reports it back to you if the file is recognized as a virus or spyware. This ensures that none of the malicious programs can escape from being detected as there are 24 different antivirus engines are involved in the scanning process.

Keyscrambler

Keyscrambler is one of the best protection against keyloggers that you can have, Keyscrambler is a small program which encrypts your typed keystrokes so even if the victim has installed a keylogger on your system, he or she will get encrypted keys. Keyscrambler currently supports Firefox, Internet explorer and other applications, however its premium version supports more than 160 applications

World’s Smallest Magnetic Data Storage


Smallest Data Storage Device
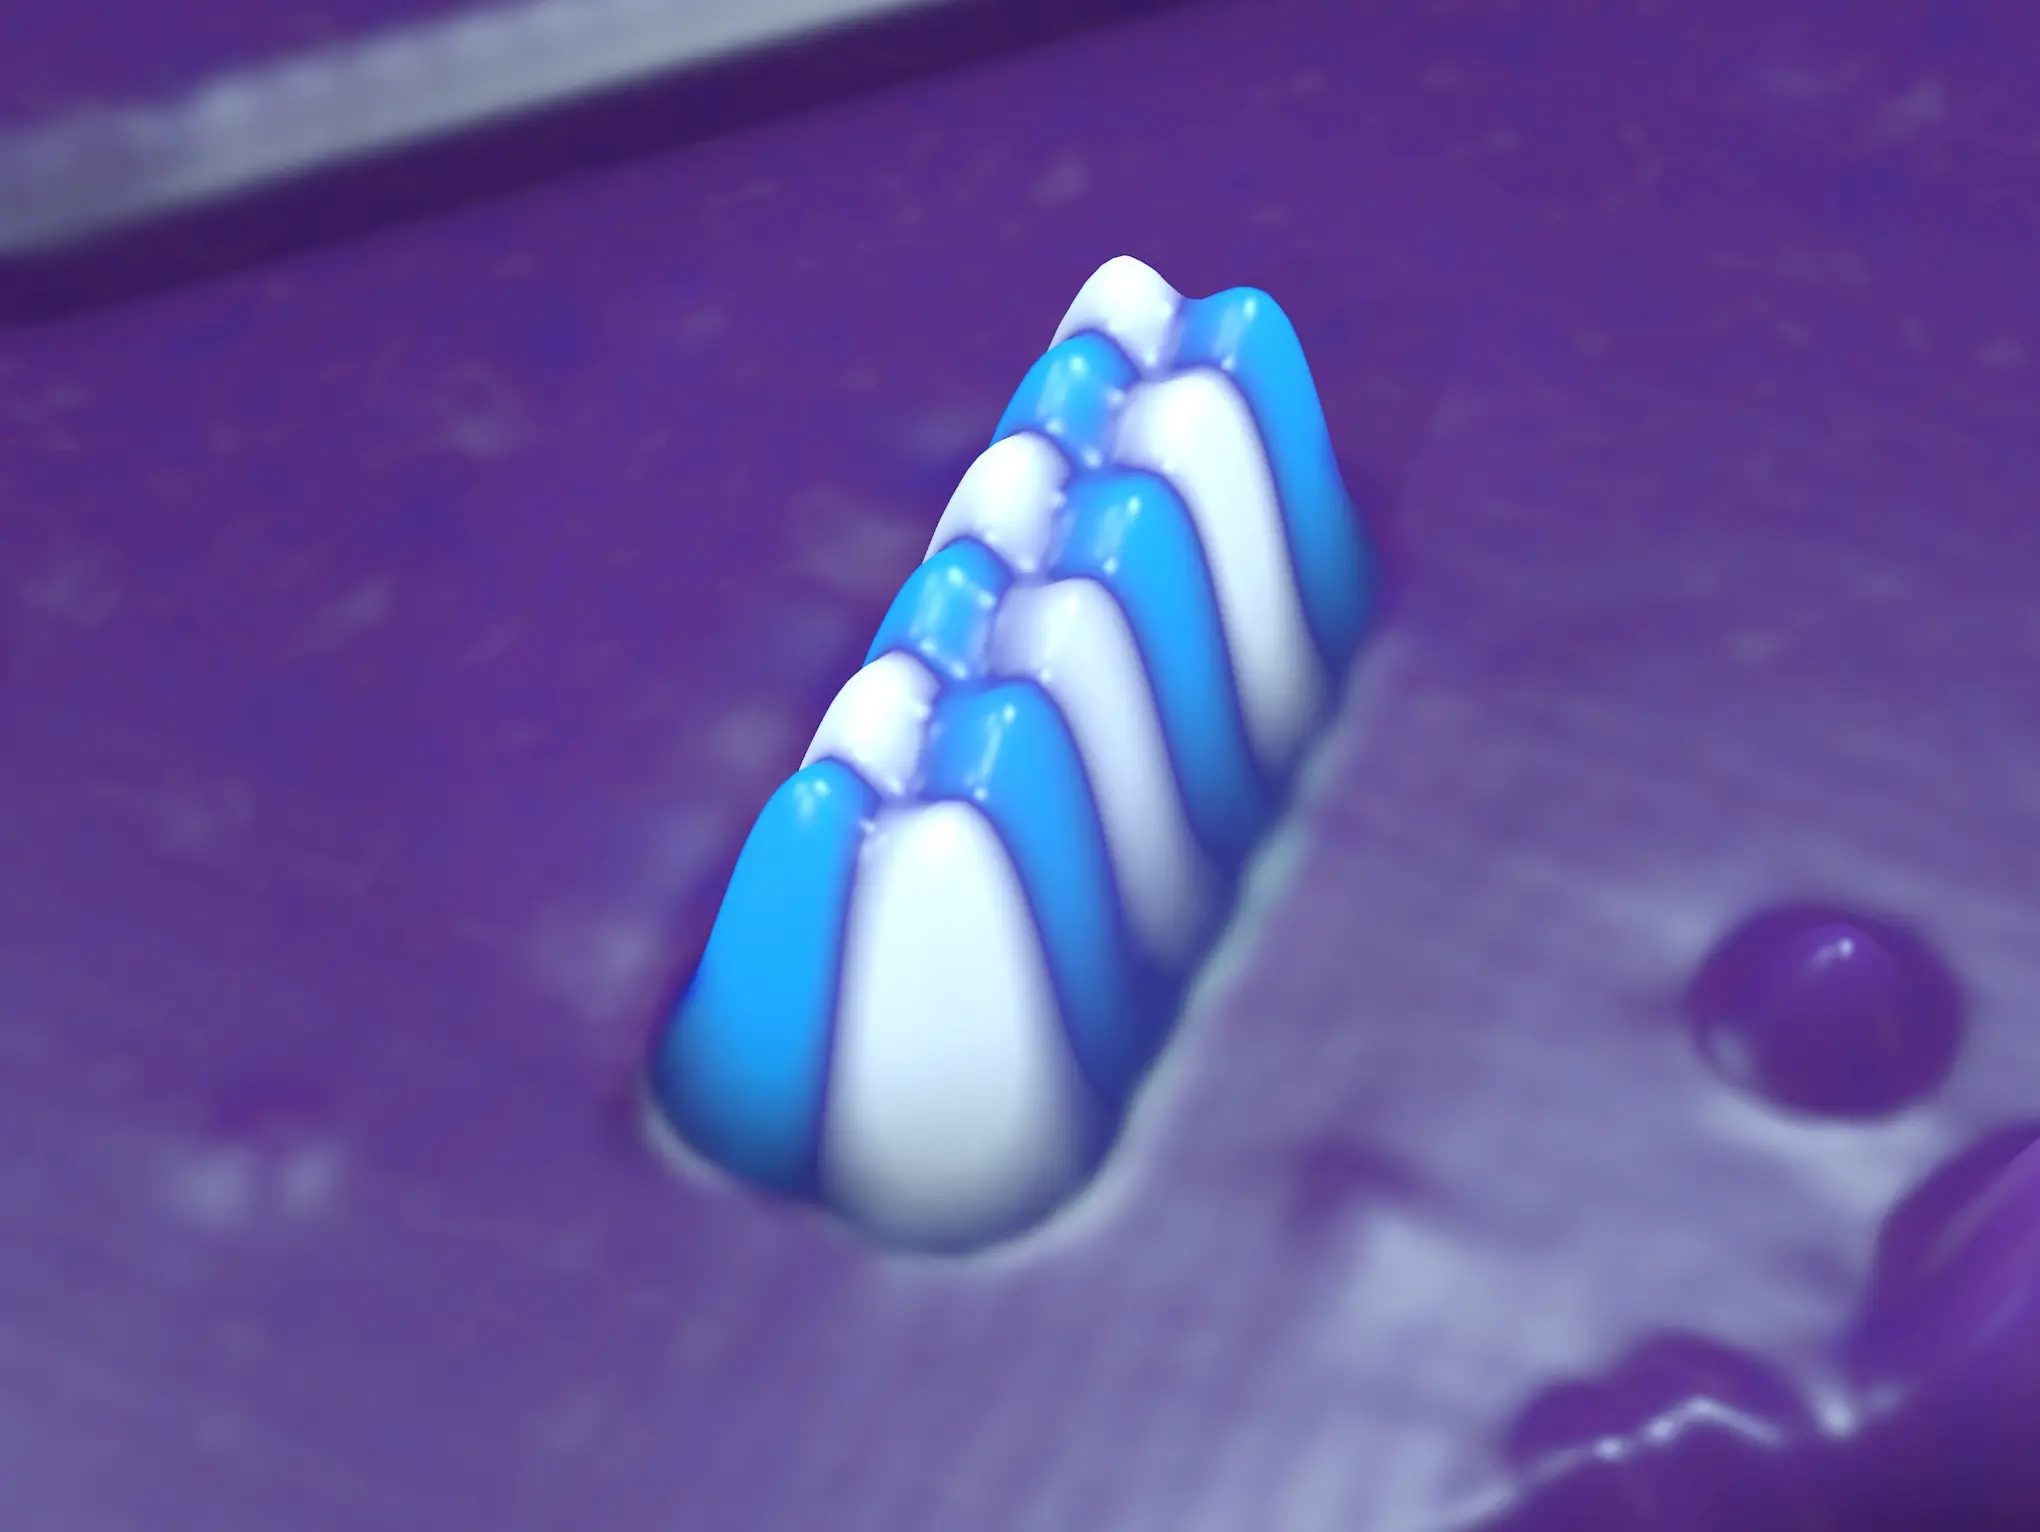
There will be a time when all the major technologies in the world will be in nanoscale. Recent developments have been undergone in daily used electronic gadgets like mobiles, computers, laptops and so on. As a part of this, a group of researchers from IBM and CFEL (Centre for free-electron Laser Science) have been successful in developing the world’s smallest magnetic data storage unit. The newly invented unit needs only 12 atoms for storing one bit. That is, 96 atoms for storing one byte. In a conventional memory storage unit a byte consists of half a billion atoms and hence this new technology will prove to be a breakthrough for producing the new generation of devices called “nanogadgets”.
This nano data storage unit was made by placing atom by atom by using a STM (scanning tunneling microscope) at IBM’s Almaden research centre in San Jose, California. First a regular pattern of iron atoms were constructed and then they were aligned in such a way that each row contains six atoms. The storage density of this nano structured memory unit is supposed to be a hundred times better than the currently used hard drives.
With the help of an STM data is written to the nano storage unit. The pairs of the atoms will be having two magnetic states representing zero and one. By using the STM the polarity of the atoms are changed to the desired value. For this purpose, an electromagnetic pulse is applied to the electrons from the STM. A weaker electronic pulse is used to read the data from the nano structure.
 In conventional hard drives and other data storage structures data is stored by ferromagnetism but here special form of magnetism called the anti ferromagnetism is used here to record data. As the materials are anti ferromagnetic, the atoms can be spaced more closely as the magnetic fields will not be interfering with each other and hence nano size can be achieved. Scientists say that this discovery will open new doors to quantum physics and smarter gadgets can be developed in the near future.

FBI surveillance backdoor might be open to hackers


This past May, according to news reports, the FBI lobbied the White House not to oppose a new piece of legislation the FBI's lawyers had drafted.
The proposed law would force companies such as Facebook, Google, Microsoft and Twitter to build "backdoors" into their software so that law-enforcement agencies could eavesdrop on communications.
But privacy advocates say building backdoors into communications software and hardware may create more problems than it solves for law enforcement — and may make the country more vulnerable to cyber attacks.
Hand over the keys
The FBI would neither confirm nor deny the existence of the legislation or its White House visit, but it's something the bureau has nonetheless been asking Congress for.

"It is critically important that we have the ability to intercept electronic communications with court approval," FBI General Counsel Valerie Caproni told a House subcommittee in February 2011. "We confront, with increasing frequency, service providers who do not fully comply with court orders in a timely and efficient manner."
Caproni cited the cases of a South American arms-trafficking ring that used encrypted communications and a pimp who lured underage girls into his prostitution ring through social networking.
The prosecution of both cases, she said, was hampered by the inability of law enforcement to eavesdrop on the suspects.
More recently, Twitter has resisted the New York City Police Department's demands that it turn over records pertaining to its users. Such headaches would be forgotten if the FBI's proposed law were to be passed. 
In December, FBI Director Robert Mueller testified to Congress that there was a real risk of law enforcement "going dark" — losing the ability to intercept communications.
"A growing gap exists between the statutory authority of law enforcement to intercept electronic communications pursuant to court order and our practical ability to intercept those communications," Mueller said.
In other words, the technology now available to criminals, terrorists and ordinary citizens is outstripping the ability of the FBI and other law-enforcement organizations to listen in.
The law as it now stands
The proposed legislation would amend a 1994 law called the Communications Assistance for Law Enforcement Act (CALEA).

CALEA is the reason the phone company can allow police to tap calls at the switching substation, where the calls are routed, rather than have someone install a bug in a house. The law was expanded in 2004 to include broadband Internet providers.
Ever since the Pretty Good Privacy encryption program for email was introduced in the early 1990s, encryption has been widely available to the general public. Encryption used to take up a lot of computing power, but the processing speed of current devices makes it easy.


The Internet-based international telephone-and-video-chat service Skype also encrypts calls, though there are ways to defeat it. Many privacy advocates worry that Microsoft's recent acquisition of Skype means that the government will soon have keys to decrypt its communications.Research In Motion's Blackberry Messenger service, for example, is so strongly encrypted that the governments of India and the United Arab Emirates have demanded the company provide the keys to decoding the messages. (RIM has partially complied.)

Even so, the FBI says there are still obstacles.
"Many communications providers are not required to build or maintain intercept capabilities in their ever-changing networks," Mueller told theHouse and Senate Judiciary Committees in May. "As a result, they are too often not equipped to respond to information sought pursuant to a lawful court order. … We must ensure that the laws by which we operate keep pace with new threats and new technology."
Basically, that means the phone companies and device makers aren't forced to build in eavesdropping ability for law enforcement.
If the FBI gets in, can hackers too?
Right now the law applies to telecom providers — phone companies — but the FBI is seeking to expand the definition. (It's important to note that nobody is looking to change the law that a search warrant be required towiretap anyone.)

That may speed up gathering evidence. But it can also leave the good guys vulnerable, said Chris Calabrese, legislative counsel at the American Civil Liberties Union in Washington, D.C.
"In Greece, the prime minister's phone calls were being tapped," Calabrese said, referring to a 2005 incident in which high-level Greek government officials found their phones had been hacked.
While it was likely that a rival intelligence agency had done it, the access to the systems was given by the same sort of "backdoor" as the FBI is seeking.
Calabrese added that it's debatable as to whether law enforcement really needs additional surveillance capabilities.
Other methods already exist — for example, encrypted communications can be tapped if an FBI agent or police officer gets access to a suspect's computer, and a keylogger would reveal all of the suspect's passwords quickly.
It's also possible to eavesdrop on communications at the "switch" level by asking a telecom provider for access.
"They can get a lot of this via AT&T," Calabrese said. "Is it really worth re-architecting the Internet?"
(Last month, nine U.S. cellular carriers revealed that they had received more than 1 million law-enforcement requests for customer data in 2011.)
Peter Eckersley, technology projects director at the Electronic Frontier Foundation, a digital-rights advocacy group in San Francisco, said the problem is that when you build any vulnerability into a system, security decreases significantly.


Stewart Baker, a former assistant secretary of policy at the Department of Homeland Security, disagreed with Calabrese and Eckersley.In other words, a built-in backdoor won't stay a secret for long, and a good hacker will learn to exploit it.

"I would not judge all lawful intercept features based on the Greek experience any more than I’d judge government management of the economy based on the Greek experience," Baker told SecurityNewsDaily in an email.
Traditional methods of surveillance are more "hit or miss," Baker said. "Keyloggers aren't as easy as you imagine."
As for the vulnerabilities introduced by backdoors, Baker said that careful monitoring can prevent them from being used by criminals or abused by law enforcement.
The power may already be there
Michael Gregg, president and chief operating officer of Superior Solutions, an IT security consulting firm in Houston, has done penetration testing and training for federal agencies, including law enforcement.

"The federal government presently has a wide array of tools that can be used to monitor voice communications, cellphones and electronic data on the Internet," Gregg said. "While built-in backdoors would make it much easier for the government to monitor communications in real time, the real question is: Would such technology be abused and used to limit free speech?"
Gregg's concerns become especially salient with the prospect of backdoors being built directly into websites. An oppressive government might use it to monitor visitors to the site.
Some new technologies actually make it easier for the FBI, or anyone else, to track where one goes online. Internet Protocol version 6, the upcoming universal Internet standard, makes it possible to link an Internet address to a machine's unique network hardware.
"Advertisers, criminals, they would all be able to see it," Eckersley said.
Some operating systems — Windows 7 and Apple's OS X and iOS among them — add  privacy features to IPv6 that generate random Internet addresses. But Eckersley noted that the implementation is not universal.
To him, that fact makes the FBI's claim that it needs new backdoors all the more surprising.